hipaa security risk assessment
$2,850
practices up to 15 staff · $3,640 for 16–40 staff
Reserve an assessment
or ring (516) 381-0450
The one most practices start with — and the one to choose if an insurer, a vendor, or your own conscience has asked whether you’ve done a risk analysis lately.
- What we look at
- Every workstation, laptop, tablet, router, and printer-scanner — including the imaging PC in the back operatory
- Who can sign in to what, and which accounts belong to people who left
- Screens visible from the waiting room, the network closet, the shred bin
- Your written policies, incident plan, and business associate agreements
- What you receive
- A dated, written risk analysis across the Security Rule’s administrative, physical, and technical safeguards
- A device and account inventory, as a spreadsheet you can keep current
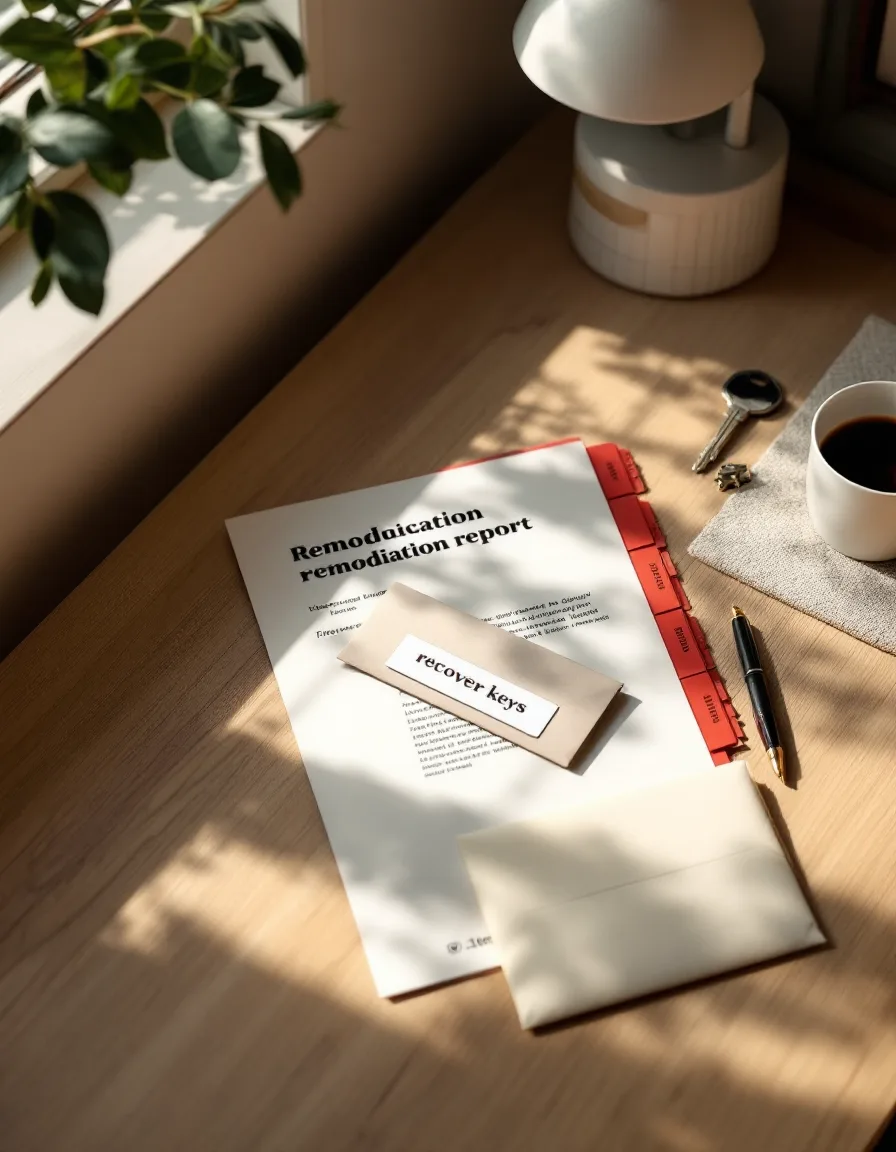
- The ranked remediation report, with the free fixes at the top
- A 45-minute walk-through of findings, then the 60-minute staff session
- Your part
- Leave a key with whoever opens, and have your list of software vendors to hand. If you can’t find your BAAs, tell us — finding them is part of the job.
- Timing
- Three to four weeks. Half a day on-site, booked before opening, over lunch, or after the last patient.